Assess, Report and Improve Your Cybersecurity Posture
Achieve compliance with ISO 27001 using automation and AI.
Enquire Now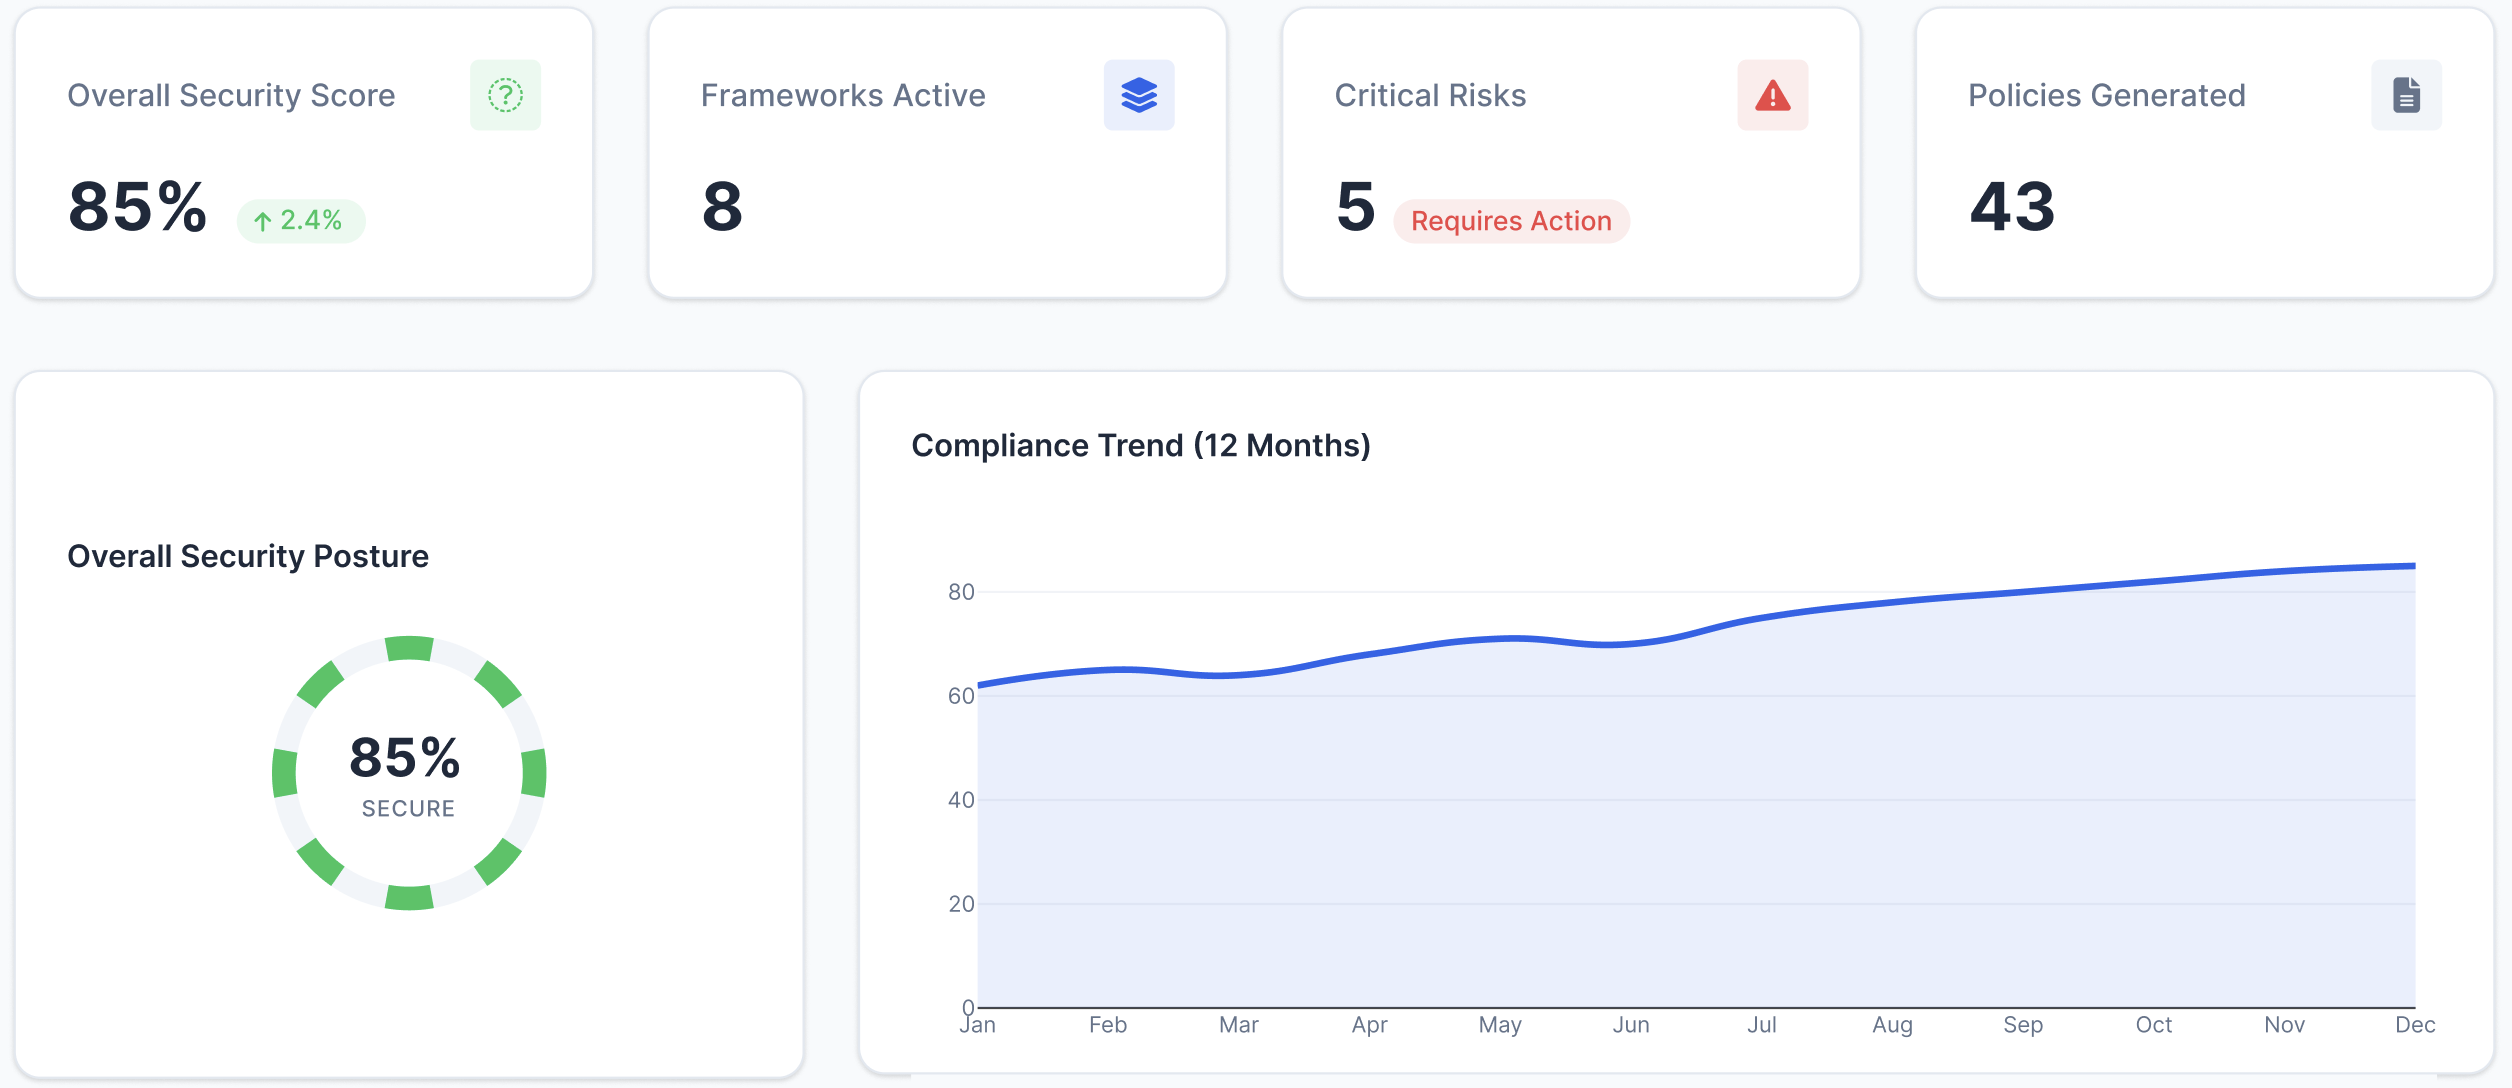
Everything you need to stay digitally resilient
A complete toolkit for managers, security officers and non-executive directors
Executive Dashboard
Real-time visibility into compliance progress.
Multi-Framework Support
ISO 27001, SOC2, NIST CSF and more.
AI Policy Generation
Generate tailored policies instantly.
Evidence Management
Upload, tag and track compliance evidence.
Automated Reporting
Generate audit-ready reports with one click.
Secure Cloud Integration
Connect AWS, Azure and Google Cloud securely.
Leverage certification frameworks to improve your cybersecurity posture
1
Assess
Assess your organisation’s cybersecurity posture in a central, structured way to measure current controls against the ISO 27001 information security standard. Understand your organisations cybersecurity stance through risk assessment, identify gaps in policies and technical controls, assign control owners and improvement actions, collect evidence of compliance, and track progress through dashboards and reports. Assessment is the first step for management and the board to understand both the organisation’s current level of security maturity and the priority actions needed to reduce cyber risk.
2
Report
Report your organisation’s cybersecurity posture through clear dashboards, risk registers and board-ready reports that show how well the organisation’s controls align with ISO 27001 requirements. Summarise the status of key controls, outstanding risks, incidents, audit findings, policy compliance, supplier assessments and remediation actions, including who is responsible and whether actions are on track. Reporting is the second step and gives management and the board a timely view of the organisation’s security maturity, areas of exposure and progress in strengthening cyber resilience.
3
Improve
Improve your organisation’s cybersecurity posture by comparing its existing policies, processes and technical controls against the requirements of the ISO 27001 standard. Highlight control gaps, such as incomplete access reviews, missing incident response testing, weak supplier assessments, outdated policies or insufficient staff training, and turn them into prioritised improvement actions. Each action can be assigned to an owner, given a due date and risk rating, supported by evidence requirements, and tracked through to completion. This final step creates a practical, transparent improvement plan that helps management focus resources on the areas that will most effectively reduce cyber risk.
Real-time Compliance Trend
Frequently Asked Questions
How does PrismGRC help with compliance?
PrismGRC automates evidence collection, policy creation and reporting.
Do you support multiple frameworks?
We currently have full integration with ISO 27001 and will soon have other control frameworks.
Is my data secure?
All data is encrypted and stored in secure cloud infrastructure.
Can I use PrismGRC to gain ISO 27001 certification?
ISO 27001 is a framework for establishing, operating, and continually improving an information security management system (ISMS) based on an organisation’s risks. It involves identifying information-security risks, applying suitable controls, documenting and monitoring them, and regularly reviewing and improving the system through audits and management review. Whilst this is not designed as a certification platform, we follow all aspects of the ISMS.